MetaMask calls almost every x402 payment a "High-risk approval"
We bought a bitcoin price for $0.001 through the Fizzl Agent Wallet, the way an AI agent does: the agent asks, the owner signs one x402 payment in their own wallet. MetaMask stopped the signature with a red alert. We tried a second, unrelated seller, and got the same alert. Neither seller's address had a security flag anywhere. The alert is about the kind of signature, not about the seller, and it fires on almost every x402 payment.
What MetaMask showed
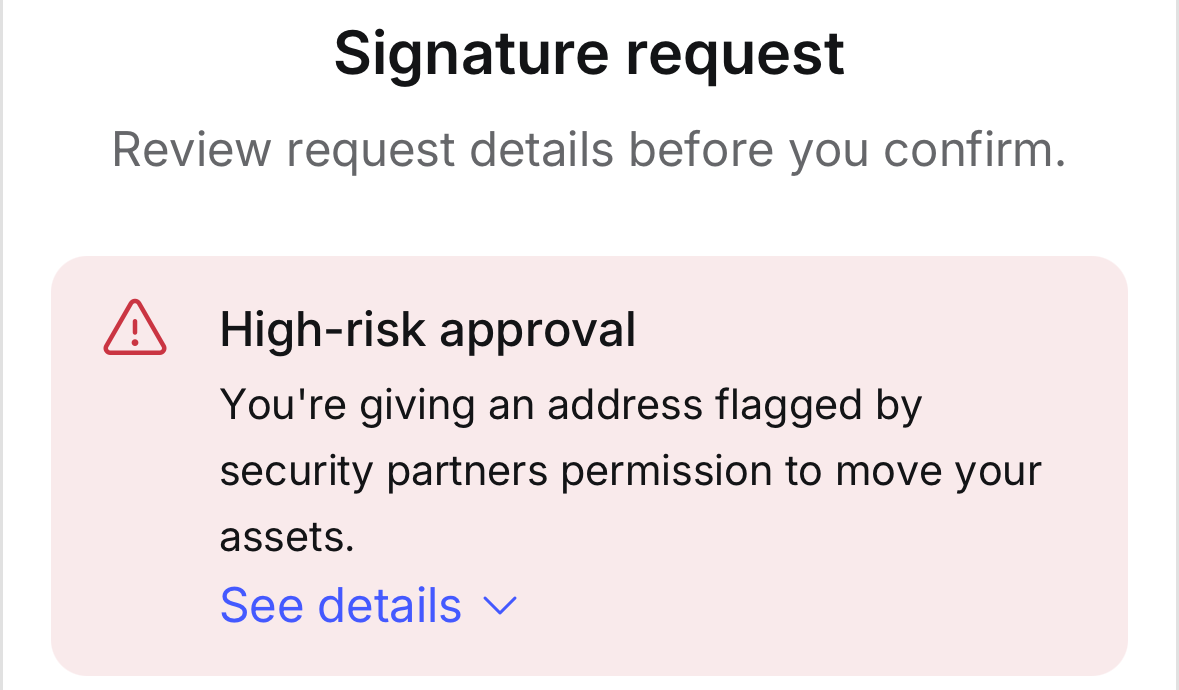
Under "See details" MetaMask gives one reason: The spender 0x… is untrusted EOA. An EOA is an ordinary wallet address, not a contract. "Untrusted" means it is on no list of known addresses, not that anyone reported it. The request type below the alert is TransferWithAuthorization on USDC, on Base.
What the signature actually does
An x402 payment on Base is an EIP-3009 TransferWithAuthorization, signed off-chain. The facilitator submits it, and USDC's own contract moves the money. These are all its fields:
| Field | Meaning | In our payment |
|---|---|---|
from | the payer | the owner's wallet |
to | the payee: the seller's payTo from the 402 | the seller's wallet |
value | the exact amount, in USDC's 6 decimals | 1000 = $0.001 |
validAfter / validBefore | the window in which it can be used | a few minutes |
nonce | random; USDC refuses the same nonce twice | one use only |
There is no allowance in it. The payee can't take more, can't take it twice and can't use it after validBefore. The worst a signature like this can do is pay that amount to that address. That is why x402 uses it: a buyer can pay a stranger without trusting them with more than the price.
Why the alert is wrong here, and where it is right
MetaMask appears to read the payment as an approval, with the payee as "spender". For approvals that rule makes sense. An approve call, an EIP-2612 Permit or a Permit2 signature hands an address an allowance it can draw on later, often for an unlimited amount. Signing one for an unknown wallet is how drainers empty accounts, and those deserve a red alert every time.
A TransferWithAuthorization is a payment, not an allowance. And x402 sellers are almost always paid to a plain wallet. Of 300 payout addresses picked at random from the 2,997 Base payout addresses in the x402 Trust Index, 289 have no contract code. Only 11 are contracts. So nearly every x402 payment signed in MetaMask meets the "untrusted EOA" rule and shows the same red alert as a drainer. An owner who has learned to stop at red stops here too. An owner who learns to click past it is worse off the day a real drainer asks for a Permit.
What is worth checking instead
The real risks of an x402 payment are not the payee's address type. They are these:
- More than the price: the
valueis higher than the 402 asked. - Someone else: the
tois not the 402'spayTo, for example a page that swapped it. - Another token or chain: the domain names another contract, or another chain id.
- Too long a window: a
validBeforemonths away leaves a signed payment lying around. - A sanctioned payee: an address on the OFAC SDN list.
presign-guard checks exactly these when it is given the signature and the 402 option being paid. A match is X402_REQUIREMENTS_MATCH. A higher or lower amount, another payee, another token or another network is red (X402_AMOUNT_ABOVE_REQUIRED, X402_RECIPIENT_MISMATCH, X402_ASSET_MISMATCH, X402_NETWORK_MISMATCH). A long validity window is orange (X402_VALIDITY_TOO_LONG). The payee is screened against the sanctions list too.
We ran the second payment through its free quick check, with a two-minute window and the seller's 402 option: green. The same payment with a validity of several months came back orange. So the check flags what matters and passes the ordinary case.
What we changed, and what wallets could change
- The Fizzl Agent Wallet's approval page now says, under the sign button for every Base payment: MetaMask may warn "untrusted EOA". This signature is not an approval: it sends exactly the price once to that address, for a few minutes. Check the address and amount in the wallet's message before you sign.
- We reported it to MetaMask as a false positive, with both payees.
- For wallet makers: show a
TransferWithAuthorizationas what it is: "pay $0.001 to 0x…, once, valid for 2 minutes". Keep the red alert forPermit, Permit2 andapprove. Better still, compare the signature with the 402 being paid, as above. - For sellers: there is nothing to fix on your side. A plain wallet as
payTois normal, and a contract only to avoid the alert would add risk.
How we checked
- Two x402 payments of 0.001 USDC on Base were requested by an AI agent (Grok, through the Fizzl Agent Wallet's MCP connector) to two unrelated sellers. Both were opened in MetaMask Mobile on 30 October 2026. Both showed the alert; the second was signed and delivered.
- Both payees checked with GoPlus's address security API (no flags) and against the OFAC SDN list (not listed). MetaMask's own site scanner rates both sellers' domains as safe ("NONE").
- 300 payout addresses sampled at random from the x402 Trust Index's Base list of 30 October 2026 (2,997 addresses), each read with
eth_getCodeon Base: 289 without contract code, 11 contracts. - presign-guard's free quick check run on the same payment with a two-minute and a several-month validity window.
We don't name the two sellers: they did nothing wrong.
Questions
Is it safe to sign an x402 payment when MetaMask says "High-risk approval"?
If the message is a TransferWithAuthorization (EIP-3009) and its to, value, token and validity match the 402 you are paying, it moves exactly that amount once and grants no allowance. Check those four fields in the wallet's message, or let a pre-sign check compare them with the 402 for you. Never sign a Permit, Permit2 or approve call because a payment page asks for it: those do grant an allowance.
Why does MetaMask call the seller "untrusted EOA"?
It reads the payment like a token approval and treats the payee as the spender. x402 sellers are almost always paid to a plain wallet (an EOA) that is on no trusted list, so the warning fires. The address carries no security flag of its own.
What should an agent or wallet check before signing an x402 payment?
That the amount, payee, token and chain in the signature equal the 402's accepted option, that the validity window is minutes rather than months, and that the payee is not on a sanctions list. presign-guard does this in one call and answers green, orange or red with reason codes.
Check a payment before you sign it with presign-guard, check the seller before you pay with x402 Doctor, and let an agent ask while you sign with the Fizzl Agent Wallet.